
On October 10, The Gateway Pundit revealed concerning video showing two alleged election workers, one carrying a toddler, entering the Maricopa County Tabulation and Election Center (MCTEC) after hours and inserting a device into a computer allegedly associated with Maricopa County’s balloting system.
Since then, questions and concerns have grown, and, despite claims of transparency from Maricopa officials, none of The Gateway Pundit’s questions have been answered or even acknowledged thus far. The Gateway Pundit has requested documents concerning the authorization, certification, and chain of custody for this software and the alleged update several times, including through open records requests submitted by other interested parties.
Maricopa County officials, at minimum, should provide the following records for this concerning late-night update:
- Any records documenting the authorization for the software installation/update, including any notification to or determination by the Secretary of State regarding whether the change required additional L&A testing, and any certification or testing records applicable to the software
- Records identifying who wrote the software update
- System log files for the time-stamped segments from the video showing precisely what was done on that terminal
- Any logs showing potential connectivity with the internet and, more importantly, any other terminals or systems
- Any inventory, access, custody, transfer, disposal, or other tracking records associated with the USB devices used during the installation.
Response below in your comments @DebbieLesko
So it’s public, I would like to see whatever forms authorized this update as well as the certification for the update. Any chain of custody records would be much appreciated as well.
Thanks in advance. You can post here, DM me or my email is in my bio.
— CannCon (@canncon) October 14, 2026
@DebbieLesko Can you post the authorization forms from the SOS or whomever authorized and certified this update? I followed so you can DM if you’d like.
— CannCon (@canncon) October 14, 2026
Patiently waiting for a response from @DebbieLesko and/or @MarkStewart_AZ
Check comments in the post where you asked for question, Vice Chair Lesko.
And check your DMs, Supervisor Stewart.
Will gladly issue corrections if I’m wrong and give you a platform to provide the answers and requested documents both on @gatewaypundit as well as @BadlandsMedia_
— CannCon (@canncon) October 16, 2026
Update: New Video Released by We The People USA Alliance
A newly released video from We The People USA Alliance now raises more questions that should be addressed by Maricopa County officials.
It should be noted that these videos were not publicly available from the Maricopa 24/7 livestream. When Shelby Robinson of We The People USA Alliance brought this video to the attention of Maricopa County officials, they seemed more concerned with how she obtained it and whether she had more in her possession.
We The People USA Alliance also shares The Gateway Pundit’s concerns regarding the inadequate production of authorization forms, system log files, as well as the lack of details about what specifically was being loaded and whether it was certified prior to installation.
A newly attained video of Maricopa County BTC room confirms that software was being installed on Oct. 7th. To date, Maricopa County has not produced any system logs or provided details on WHAT software was being loaded or that software has been certified and approved for use prior to install.
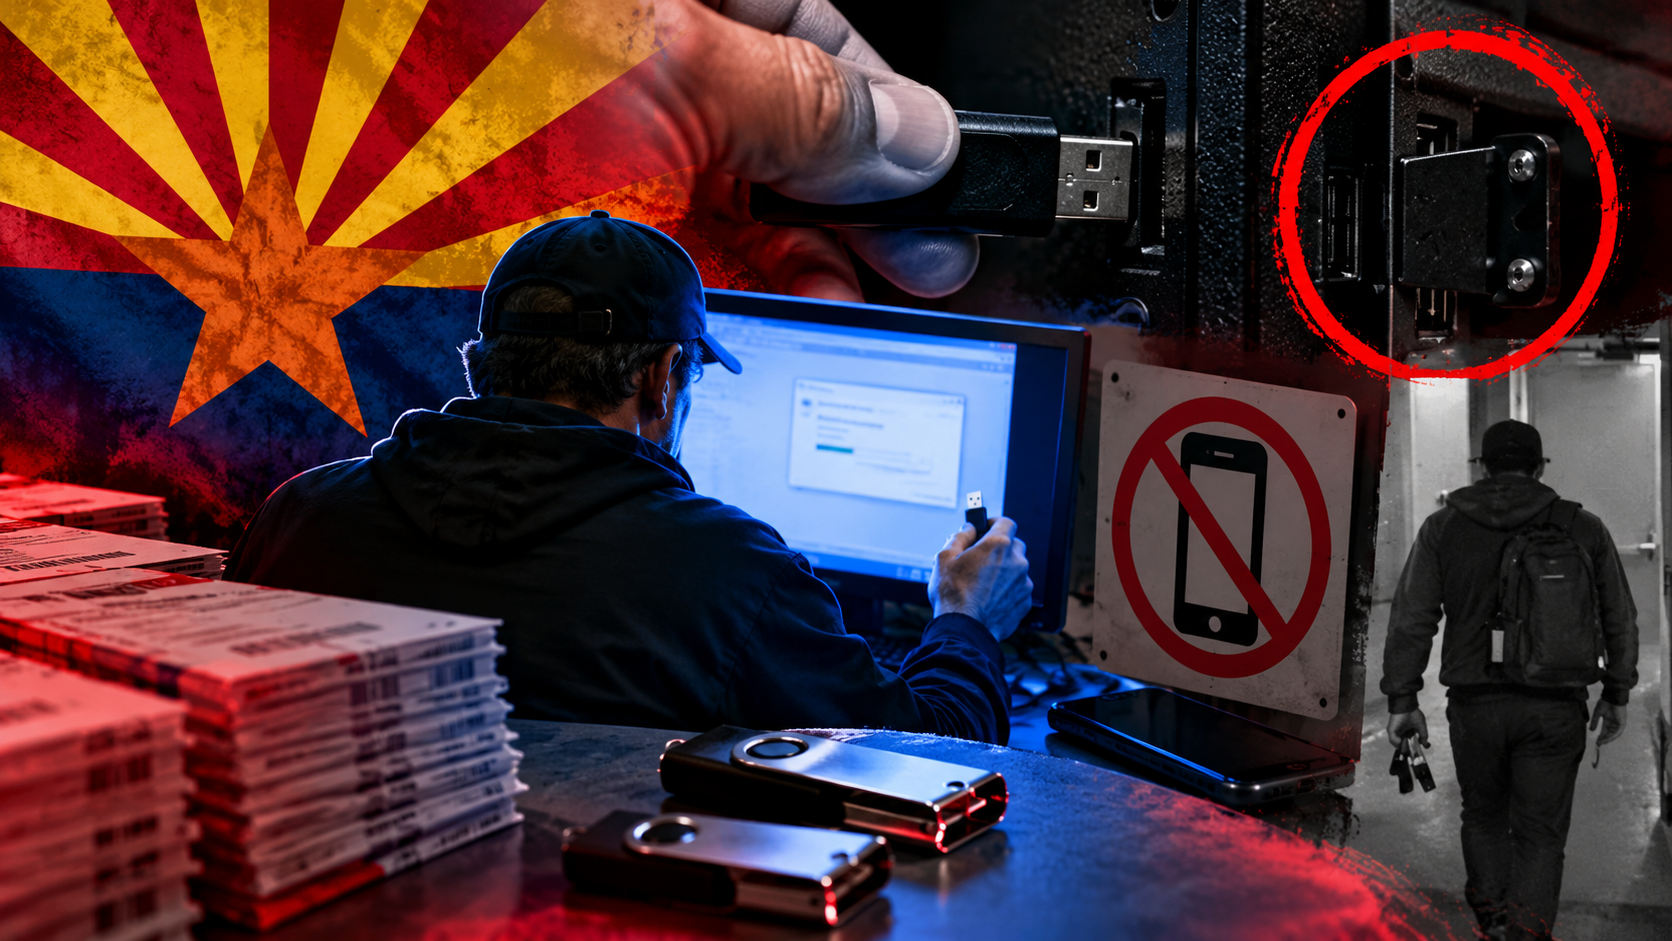
SECURITY ALERT: Video shows failure to secure port blockers, secure keys or log and track USB drives in accordance with security protocols. *Video shows the employee leaving the room and the facility in position of the flash drive with NO chain of custody.
Maricopa County needs to provide answers: Was this the Runbeck Novas Duplication Software being loaded and has it been certified and approved? Would a file naming error as presented in the demonstration require a software update/install?
— We the People USA Alliance (@WethePeopleAZA1) October 17, 2026
The new video from the election integrity group shows more than one USB being utilized for the “software update.” The election employee can be seen inserting at least two USB devices into the terminal accessed through the unsecured port blocker.
Following the insertion of the devices, zoomed-in video appears to show Windows Installer being run. It is also notable that the terminal on which this work is being performed is the only visible unit that seems to have the computer tower under the monitor and accessible to staff when the port blocker is unsecured.
Once the installation was complete, the employee left the building with the USB devices. It is unclear whether they were stored or disposed of in another part of the building off camera.
Another concerning observation is the presence of a cell phone. The employee places his cell phone directly next to the terminal during the installation. Signs at the end of the row clearly state “No Electronics” and, more pointedly, “No Cell Phones.” Cell phones can be used to set up independent Wi-Fi hotspots to which a Windows-based computer could potentially connect, however, the simple presence of a cell phone does not establish that the computer was connected.
Now, why would you not want cell phones in an “air-gapped” room? https://t.co/4i97NMEoq6
— CannCon (@canncon) October 21, 2026
The voting systems in Maricopa County had already undergone logic and accuracy (L&A) testing just days earlier to ensure the public that the machines were accurately tabulating ballots during the test. Despite that demonstration, many cybersecurity and election experts have questioned the value of such public testing, asserting that the systems can be programmed to recognize testing and perform differently during that period.
In a previous article, The Gateway Pundit documented questions surrounding whether electronic ballot-duplication software is subject to Logic & Accuracy testing requirements.
The Arizona Elections Procedures Manual does not expressly authorize stand-alone electronic ballot-duplication software. In fact, the EPM states that damaged or defective ballots that cannot be scanned by tabulation equipment “must be manually duplicated” by a Ballot Duplication Board.
The EPM does separately authorize the use of a “certified electronic adjudication program” as an alternative or addition to manual ballot duplication for certain votes requiring adjudication. But that application must be part of a federally and state-certified Election Management System (EMS), and its electronic-adjudication functionality must undergo L&A testing when it will be used in an election.
That distinction raises two important questions:
- If stand-alone ballot-duplication software performs functions that would otherwise be performed manually, is that software subject to certification and L&A testing requirements?
- If it is not, what provision of the EPM or Arizona law authorizes the use of stand-alone electronic ballot-duplication software in place of the manual duplication process prescribed by the EPM?
Last week, We The People USA Alliance co-founder Shelby Robinson (formerly Shelby Busch) joined the Badlands Media ‘Why We Vote’ podcast to discuss the event.
During the interview, Robinson disclosed additional information related to the situation.
As reported earlier, Robinson believes one of the election workers was a Maricopa County election worker who had previously accessed the county’s system before the audit that was conducted in 2021 following the controversial 2020 presidential election.
According to Robinson, security logs show that a different employee’s badge was used to access the server and that files were “archived” and then deleted. This was controversial because all election records had been subpoenaed by the Arizona Senate for the audit.
When auditors discovered that more than one million election-related files had been deleted, Maricopa County officials claimed those files had been “archived” rather than deleted. Still, they were never voluntarily turned over to the auditors, but one of the contracted auditors was reportedly able to recover the files.
Robinson also claims that the election worker seen working at the terminal left the building with those flash drives, as well as the keys to the port blockers. Port blockers are devices used to protect USB ports on the terminals, especially after certification and L&A testing are complete. These are important security devices intended to prevent unauthorized devices from being inserted into the system once the machines have been certified for the election.
Maricopa County should identify precisely how it classifies the Novus system under Arizona’s EPM. If it is part of the certified EMS, tabulation system, or electronic voting system, the EPM imposes significant requirements concerning certification, L&A testing, post-L&A changes, removable media, network isolation, credentials, and logging.
If it is not part of those systems, the County should identify the authority permitting standalone electronic ballot-duplication software where the EPM expressly describes damaged or defective ballots as being manually duplicated by a bipartisan Ballot Duplication Board.
The post NEW FOOTAGE: USBs, Unsecured Ports and a Cell Phone Inside Maricopa Ballot Tabulation Center appeared first on The Gateway Pundit.